Iris Otto · 30 September 2026
Navigating Encryption Protocols for Secure Annotation Sharing Across Multi-Team Digital Notebook Ecosystems in Regulated Industries
Regulated industries such as pharmaceuticals, finance, and healthcare rely on digital notebook ecosystems to manage collaborative annotation work across distributed teams, and these platforms demand robust encryption to protect sensitive data during sharing, storage, and retrieval processes. Experts observe that annotations often contain proprietary research details, patient information, or financial models, which makes protocol selection critical for compliance with standards set by bodies including the National Institute of Standards and Technology and the European Medicines Agency. Teams must balance usability with security measures that prevent unauthorized access while allowing seamless cross-team contributions, and this balance becomes especially relevant as organizations prepare for updated data protection frameworks scheduled to take effect in September 2026.
Core Encryption Standards in Multi-Team Environments
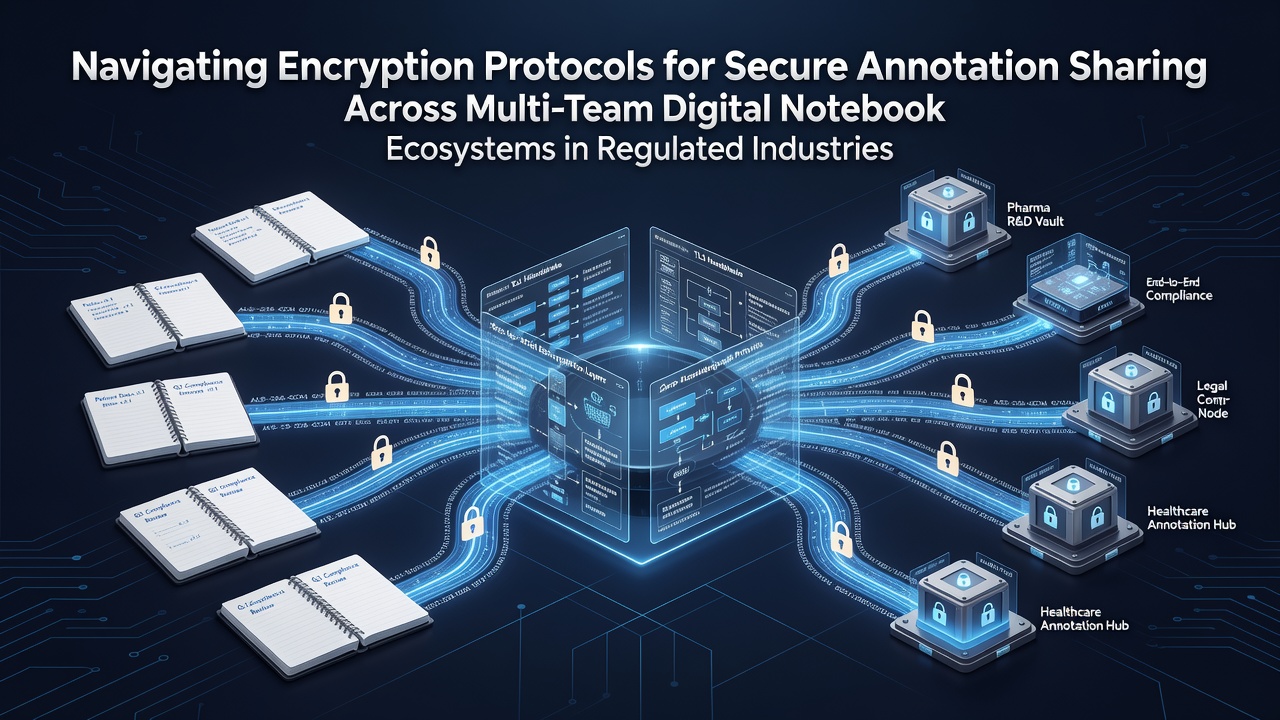
Advanced Encryption Standard with 256-bit keys serves as the foundation for most secure notebook systems because it delivers efficient symmetric encryption that scales across large annotation datasets without introducing noticeable latency. Researchers have documented how AES-256 integrates with asymmetric methods like RSA or Elliptic Curve Cryptography to handle key exchanges between teams operating in separate jurisdictions, and this hybrid approach ensures that annotations remain confidential even when shared through cloud-based repositories. Organizations in Canada and Australia have adopted similar frameworks to align with local data residency rules, which demonstrates the global push toward interoperable encryption that meets multiple regulatory requirements simultaneously.
Challenges of Annotation Sharing in Distributed Ecosystems
Multi-team setups introduce complexities because annotations generated in one notebook instance often need to sync with others in real time, and any encryption mismatch can lead to access denials or data corruption during transfer. Studies from academic institutions reveal that metadata attached to annotations, such as timestamps and contributor identifiers, requires separate protection layers to avoid leakage that could compromise the entire dataset. Teams working across time zones face additional hurdles when key rotation schedules differ, yet solutions like automated key management services help maintain consistency while complying with audit trails demanded by regulators. What's notable is that end-to-end encryption models prevent intermediaries from viewing content, but they also demand careful planning around user authentication to avoid workflow bottlenecks.
Integration with Regulatory Compliance Requirements
Data from the U.S. Food and Drug Administration shows that audit-ready encryption logs form a mandatory component of electronic record systems in life sciences, and similar expectations appear in financial services under frameworks from the Australian Securities and Investments Commission. Protocols must support features like granular access controls and immutable change histories so that annotations cannot be altered without detection, and this capability aligns with broader goals of maintaining data integrity across ecosystems. Organizations that implement these measures report fewer compliance incidents, though implementation costs vary depending on whether legacy notebook tools require retrofitting or complete replacement.
Emerging Approaches and Protocol Evolution
Post-quantum cryptography options gain traction as organizations anticipate future threats from quantum computing, and researchers note that lattice-based algorithms offer promising resistance while remaining compatible with existing notebook architectures. Hybrid deployments that combine classical and quantum-resistant methods allow gradual migration without disrupting ongoing annotation projects, and this strategy appears in pilot programs run by European research consortia. Automated policy engines further assist by enforcing encryption rules based on annotation sensitivity levels, which reduces human error in multi-team settings where contributors may overlook classification requirements. Data indicates these tools improve adherence rates when integrated directly into notebook interfaces rather than applied as afterthought overlays.
Practical Implementation Across Industries
Pharmaceutical companies often deploy containerized encryption modules that wrap individual annotation entries, enabling selective decryption only for authorized reviewers while keeping the broader notebook collection protected. Financial institutions follow comparable patterns but emphasize real-time monitoring of key usage to detect anomalies that could signal breaches during collaborative modeling sessions. Observers point out that training programs focused on protocol awareness help teams avoid common pitfalls such as weak passphrase choices or improper sharing of decryption credentials, and these educational efforts complement the technical safeguards already in place. Case examples from regulated sectors illustrate how standardized key escrow procedures support both security and business continuity when personnel changes occur across partner organizations.
Conclusion
Effective navigation of encryption protocols requires ongoing attention to evolving standards, regulatory timelines, and technical integrations that support secure annotation workflows in complex multi-team environments. Organizations that align their digital notebook strategies with established guidelines from diverse international bodies position themselves to handle current demands while preparing for developments expected in September 2026. Continued research and cross-industry collaboration will shape the next generation of solutions that maintain both protection and productivity in these critical ecosystems.